Single Sign-On (SSO)
Connect your corporate identity provider to FinologeeBKO with OpenID Connect or SAML 2.0
Introduction
Single Sign-On (SSO) lets users sign in to FinologeeBKO with the credentials of their corporate identity provider. Users do not need a separate FinologeeBKO password, and your IT department keeps control of access policies, password rules and multi-factor authentication in its own identity management system.
FinologeeBKO connects to your identity provider through the Finologee IDP, the identity layer operated by Finologee. You register FinologeeBKO as an application in your identity provider, send a few values back to Finologee, and Finologee completes the connection on its side.
This page gives the overview. The step-by-step configuration for each protocol is on its own page:
Supported protocols
| Protocol | Description |
|---|---|
| OpenID Connect | Identity layer on top of OAuth 2.0. Your identity provider issues an ID token that identifies the user. |
| SAML 2.0 | Security Assertion Markup Language version 2.0. Your identity provider issues a signed SAML assertion that identifies the user. |
Supported identity providers
FinologeeBKO works with any identity provider that supports OpenID Connect or SAML 2.0. The configuration has been tested with:
- Microsoft Entra ID (formerly Azure Active Directory)
- Okta
- Keycloak
If you use another identity provider, follow the generic instructions on the protocol pages. The values to register are the same for every provider.
Choosing a protocol
Both protocols are supported. For new setups we recommend OpenID Connect.
| OpenID Connect | SAML 2.0 | |
|---|---|---|
| Configuration | Simpler: a redirect URI, a client ID and a client secret | More settings: entity ID, reply URL, NameID format and attribute statements |
| Signing keys | Your identity provider publishes its signing keys and rotates them automatically | Your identity provider's signing certificate expires and must be rolled over in coordination with Finologee |
| Credential to maintain | A client secret with an expiry date, which you must renew before it expires | The signing certificate described above |
| When to choose it | Default choice for new connections | When your internal policy requires SAML 2.0 |
Setting up a connection
Each SSO connection between your identity provider and FinologeeBKO is set up in six steps.
- Tell Finologee which protocol you want to use: OpenID Connect or SAML 2.0.
- Finologee sends you the connection identifier and the values to register in your identity provider.
- Configure your identity provider by following the protocol page: OpenID Connect or SAML 2.0.
- Send Finologee the items listed in "What to send to Finologee" on the protocol page.
- Finologee completes the connection and enables SSO on your tenant.
- Test the connection together in the sandbox environment, then repeat the setup for production. Register the sandbox values in your identity provider as a separate application, with its own client secret or signing certificate.
User-level enablement
Once the connection is in place, an administrator enables SSO for each user in User & Groups. The email address of the FinologeeBKO user must be identical to the email address your identity provider sends. SSO users need no other credentials. A second authentication method can be added for users who need a higher level of signature, for example LuxTrust.
Attribute mapping
FinologeeBKO needs very little information from your identity provider:
| Attribute | Status | Notes |
|---|---|---|
| Email address | Required | Must be identical to the email address of the user in FinologeeBKO. This is how FinologeeBKO recognises the user. |
| First name | Recommended | Used for the user's display name. |
| Last name | Recommended | Used for the user's display name. |
| Stable user identifier | Automatic | Sent by every compliant identity provider. No configuration is needed. |
Nothing else is needed. Groups, roles and app roles from your identity provider are not used. Authorisation stays in FinologeeBKO, through User & Groups and signatory rules.
Multiple SSO providers per tenant
A single FinologeeBKO tenant can have several SSO connections, one per identity provider.
Multi-provider scenarios
Several connections are useful for:
- Fund administrators: different funds sign in with their own corporate identity providers
- Multi-organisation tenants: users from partner companies or subsidiaries use their own identity providers
- Mergers and acquisitions: separate identity providers remain in place during a transition
- Client access: clients use their own SSO while internal staff use a separate provider
Provider selection
When several connections are configured:
- Each connection has its own button on the login screen, with a label and optionally a logo
- Users select the button of their organisation
- Authentication continues at the selected identity provider
Configuration considerations
- Each connection is configured separately and has its own connection identifier
- Each connection has its own credentials: a client secret for OpenID Connect or a signing certificate for SAML 2.0
- Button labels should clearly identify the organisation
- Each connection should be tested on its own
User management
- The email address identifies the user in FinologeeBKO
- Permissions and access control are defined at tenant level, not per identity provider
- Users from different identity providers can work together in the same tenant
Authentication flow
SSO uses a redirect-based flow. Users authenticate at your identity provider, with the security controls you already apply there.
Onboarding flow
When the administrator enables SSO as an authentication method for a user, the authentication method is active immediately. The user receives a welcome email with a link to the FinologeeBKO login page and can log in straight away with their corporate credentials. No OTP confirmation step is required for SSO activation.
Why SSO does not require OTP activationThe purpose of OTP activation for other authentication methods is to confirm access to the email address. For SSO, this confirmation is implicit: users cannot authenticate through their corporate identity provider without access to the corporate account associated with that email address.
Login process
- The user opens the FinologeeBKO login page.
- The user selects the button of their identity provider, for example "Microsoft".
- The Finologee IDP redirects the user to your identity provider.
- The user authenticates at your identity provider with their corporate credentials.
- Your identity provider returns an ID token (OpenID Connect) or a SAML assertion (SAML 2.0) to the Finologee IDP.
- The Finologee IDP validates the response, FinologeeBKO recognises the user by email address and grants access.
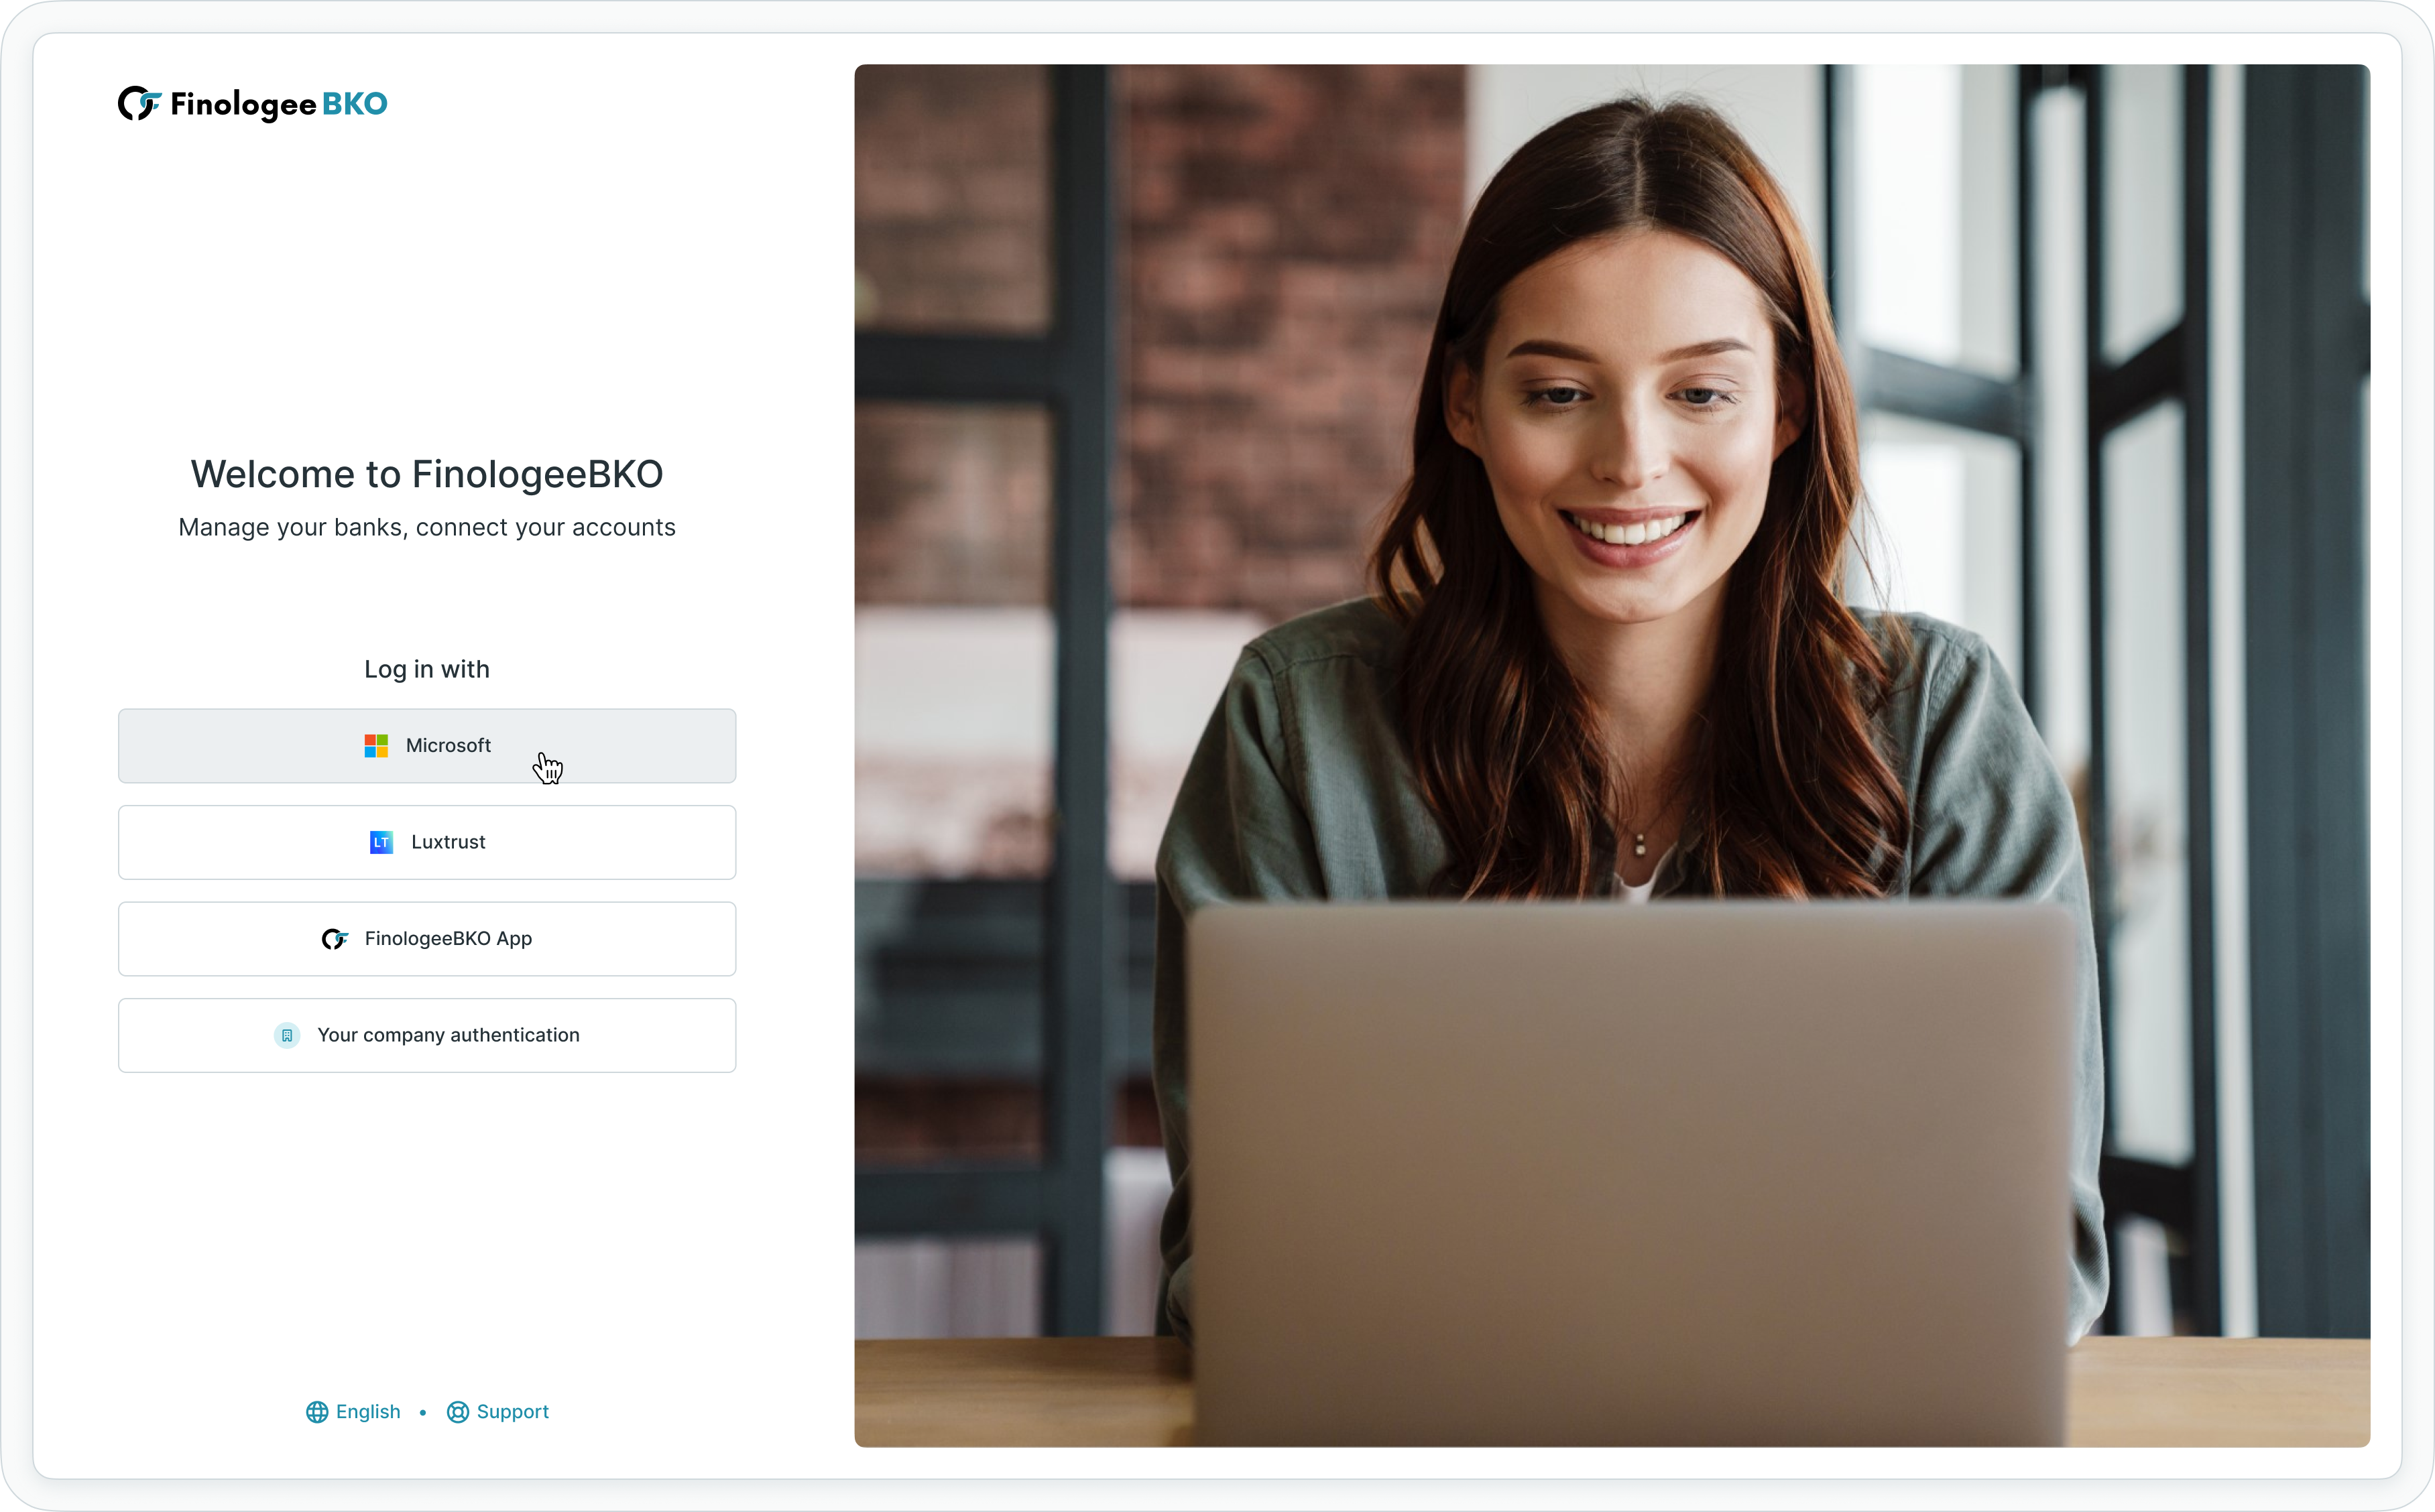
SSO login screen showing Microsoft authentication option
Token validation
The Finologee IDP checks every response from your identity provider before FinologeeBKO grants access:
- The signature, against your identity provider's published keys or signing certificate
- The issuer, which must be your identity provider
- The audience, which must be the FinologeeBKO connection
- The validity period, so that expired responses are rejected
Signature capabilities
SSO provides simple electronic signatures for transaction authorisation within FinologeeBKO. As explained in Digital Signatures, SSO-based signatures are simple electronic signatures under eIDAS: they represent authenticated consent but provide limited technical guarantees.
Simple electronic signatures
SSO-based signatures offer:
- Authentication-based consent: the user's identity is verified through corporate SSO
- Audit trail: signature events are logged
- User identity: the signature is tied to the user authenticated by your identity provider
- Timestamp: the time of each signature is recorded
Signature limitations
Organisations that need a higher level of signature assurance should note:
- SSO signatures are simple electronic signatures under eIDAS (equivalent to a click after authentication)
- OpenID Connect and SAML 2.0 do not define electronic signature mechanisms
- High-value transactions may require LuxTrust qualified signatures
- Regulatory requirements may mandate stronger signature methods
- Some industries require qualified electronic signatures for specific transaction types
Combined authentication strategies
Users can have several authentication methods to balance convenience and security:
- SSO for login: daily access with corporate credentials
- LuxTrust for high-value signatures: qualified signatures for payments above thresholds
- FinologeeBKO mobile app for mobile signatures: advanced signatures for mobile workflows
Multi-tenant configuration
Users with access to several tenants may have a different authentication configuration in each tenant.
Per-tenant authentication
- Authentication methods are tenant-specific
- A user can have SSO for Tenant A and LuxTrust for Tenant B
- SSO connections are configured per tenant
- Users switch tenants after the initial authentication
Cross-tenant considerations
Organisations with several FinologeeBKO tenants should consider:
- Using the same identity provider across tenants
- A single user provisioning approach for all tenants
- Access control policies that apply across tenants
- Session handling when users switch tenants
Common questions
Getting started
What do I need to use SSO with FinologeeBKO?
An identity provider that supports OpenID Connect or SAML 2.0, such as Microsoft Entra ID, Okta or Keycloak. Your IT administrator registers FinologeeBKO in the identity provider, following the OpenID Connect or SAML 2.0 page, and Finologee completes the connection.
Can I use my existing corporate credentials?
Yes. You use the same username and password as for the other corporate applications connected to your identity provider.
Do I need to remember a separate password for FinologeeBKO?
No. You authenticate with your corporate credentials, which your IT department manages according to your organisation's password policies.
Using SSO
What happens if I cannot access my corporate account?
Contact your IT department, as FinologeeBKO authentication relies on your corporate identity provider. Your FinologeeBKO administrator can also configure a second authentication method for critical users.
Can I use SSO on mobile devices?
Yes. SSO works in the mobile browser. You are redirected to your identity provider's login page, as on a desktop.
Why do I see several SSO buttons?
Your tenant has several SSO connections, for users from different organisations. Select the button of your organisation.
Security
Is SSO secure?
SSO uses the OpenID Connect or SAML 2.0 standard. Every response from your identity provider is signed and checked before access is granted. Security is stronger when your identity provider enforces multi-factor authentication and strong password policies.
Can administrators see my corporate password?
No. Your password never passes through FinologeeBKO. You authenticate directly at your identity provider, which then confirms your identity to FinologeeBKO.
What happens if my corporate account is compromised?
Your IT department can disable your account at the identity provider, which prevents new logins to FinologeeBKO and to all other connected applications.
Best practices
Security considerations
- Enable multi-factor authentication at your identity provider
- Apply conditional access policies for sensitive operations
- Restrict the FinologeeBKO application to the users who need it
- Review user access and permissions regularly
- Monitor authentication logs for suspicious activity
- Revoke access promptly when a user leaves
User experience
- Give first-time SSO users clear instructions
- Consider a second authentication method for critical users
- Test the login flow before rolling SSO out to all users
- Announce maintenance windows and identity provider changes
Integration management
- Record the settings of each connection, including the expiry date of client secrets and signing certificates
- Keep the sandbox and production applications separate
- Test configuration changes in the sandbox first
- Keep the contact details of your identity provider administrators up to date with Finologee
- Agree an escalation procedure for authentication issues
Multiple provider management
- Record which users belong to which identity provider
- Agree clear labels for the login buttons
- Test each connection on its own before production
- Coordinate changes with the administrators of each identity provider
- Keep a support contact for each identity provider
Related documentation
SSO configuration:
- SSO with OpenID Connect - Values to register, what to send to Finologee, and examples for Microsoft Entra ID, Okta and Keycloak
- SSO with SAML 2.0 - Values to register, what to send to Finologee, and examples for Microsoft Entra ID, Okta and Keycloak
Core Concepts:
- Permissions - User access control and permission assignment
- Approvals - Approval workflow concepts and signature requirements
Platform Features:
- User & Groups - User creation and SSO enablement
Security & Authentication:
- Authentication Methods - Overview of all authentication options
- LuxTrust - Qualified electronic signatures for high-value transactions
- FinologeeBKO Mobile App - Mobile authentication alternative
- Digital Signatures - Transaction signing and signature validation
- Compliance & Audit - Audit trails and compliance
Support
For help with SSO configuration or identity provider integration, contact the FinologeeBKO support team at [email protected].
An SSO connection needs coordination between your IT department, your identity provider administrators and FinologeeBKO support, in particular for the sandbox test and for secret or certificate renewals.
Updated about 13 hours ago